MFA for small business: passkeys, security keys and a 30-day rollout plan
Account takeover is now the top threat facing French businesses. Multi-factor authentication stops it almost every time, provided you pick the right method, start with the right accounts and lock down account recovery.
Monday morning, your bookkeeper receives an email from a regular supplier: new bank details, please update your records. The message really does come from the supplier’s address. Their mailbox was hacked the week before with nothing more than a password, and the attacker is now using it to divert your payments. In France, this is the number one threat to businesses.
Two-factor or multi-factor authenticationMulti-factor authentication (MFA)A login that requires at least two proofs of identity of different kinds (something you know, something you have, something you are), so that a stolen password is no longer enough. (MFA) is the most effective and cheapest defence. This guide helps you choose the right method, roll it out in 30 days in a small business, and avoid the mistake attackers exploit most: a sloppy account recovery process.
Why a password alone is no longer enough
A password is a secret shared with dozens of services, and it only takes one of them to lose it. Cybermalveillance.gouv.fr, the French government’s victim support service, keeps seeing the same entry points: phishing, weak passwords, passwords reused on a breached site, compromised devices.
- Breaches and credential stuffing. Stolen databases circulate, and bots automatically try every username and password pair on other services: this is credential stuffingCredential stuffingAn automated attack that tries large numbers of username and password pairs stolen elsewhere against a site, betting that people reuse the same passwords.. The password for a hobby site becomes the password for your business email.
- Infostealers. An infostealerInfostealerMalware built to quickly steal saved passwords, session cookies, cryptocurrency wallets and browser data, which are then sold on criminal marketplaces. is malware, often hidden in a trojanised free download, that harvests passwords saved in the browser. It also steals session cookies: as the French CERT-FR pointed out back in 2022, a stolen session is already authenticated and can bypass MFA.
- PhishingPhishingA scam that impersonates a trusted sender (a bank, a supplier, a colleague) by email, text message, phone call or QR code to trick the victim into clicking, handing over credentials or paying.. Why guess a password when you can simply ask for it on a fake login page?
Which accounts to protect first
Start with the accounts whose compromise would cost you most:
- Admin accounts: the Microsoft 365 or Google Workspace console, your hosting provider, domain registrar, firewall and backups.
- Email: it is used to reset every other password and to deceive your customers. The same report records a 93% rise in payment diversion fraud against businesses, often following an email account takeover.
- Remote access: VPN, remote desktop, home-working portals.
- Banking: banks already apply strong customer authentication under the EU Payment Services Directive (PSD2). Your job is to activate the approval app for every authorised person and to require dual approval for large transfers.
- Online tools: accounting, payroll, CRM, company social media, booking or sales platforms.
SMS, app, push, FIDO2 key, passkey: how they compare
Every method blocks a stolen password. Not all of them survive a fake site that relays what you type to the real one in real time.
| Method | Phishing resistance | Cost | Day-to-day ease |
|---|---|---|---|
| SMS code | Low: code can be intercepted, number hijacked, code typed into a fake site | None | Very easy, but depends on mobile coverage |
| Authenticator app (6-digit TOTP code) | Medium: the code can be typed into a fake site | Free | Easy, works offline |
| Push notification with number matching | Medium: stops MFA fatigue, not a relaying fake site | Often included in your subscription | Very easy |
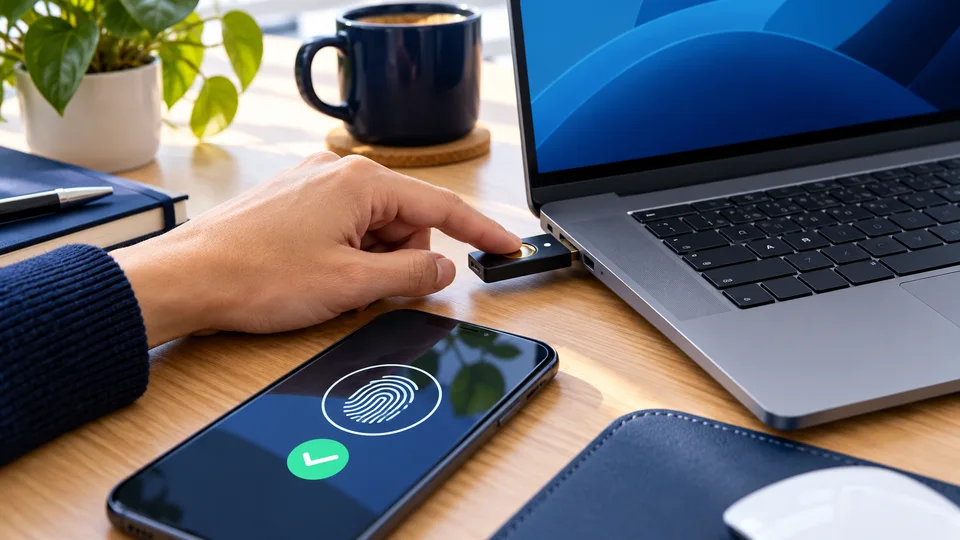
| FIDO2 security key | Strong: the key only signs for the genuine domain | One hardware key per person, two for administrators | A touch, but you must carry it |
| Passkey | Strong: bound to the domain, nothing to type | None on recent devices | Easiest: fingerprint, face or device PIN |
CISA, the US cybersecurity agency, notes that phishing-resistant methods are not susceptible to MFA fatigue or SIM swapping. A passkeyPasskeyA password-free sign-in credential based on a pair of cryptographic keys: the private key stays on your device and is unlocked with your fingerprint, face or PIN. relies on the same FIDO2 and WebAuthn standards as a security key: it lives on your device or is synced by a password manager, whereas a hardware key never leaves your pocket.
SMS and MFA fatigue
ANSSI is unequivocal: it recommends not using SMS to receive an authentication factor, because of weaknesses in phone networks and SIM swap fraud. Push notifications, for their part, spawned an attack of their own: MFA fatigue, where the victim is bombarded with approval requests until they give in.
The fix exists: require users to type a number shown on the screen, which Microsoft Authenticator now enforces, and teach everyone to reject any request they did not trigger.
The 30-day rollout plan
Week 1: administrators
- List your critical accounts and who holds them.
- Separate admin accounts from everyday accounts, following the principle of least privilegeLeast privilegeThe principle that every user, application or service receives only the rights strictly needed for its job, and only for as long as it needs them..
- Give each administrator two FIDO2 keys, or a passkey plus a backup key. Microsoft already requires MFA to sign in to its admin portals (Azure, Entra and Intune since October 2024, the Microsoft 365 admin centre since February 2025), and Google enforces it for Workspace administrators.
Week 2: email
- Microsoft 365: without an Entra ID P1 licence, turn on security defaults (free). They require everyone to register for MFA, always require it for administrators, and block legacy email protocols (IMAP, POP and SMTP with basic authentication), which would otherwise let attackers bypass MFA. With a P1 licence, use Conditional Access.
- Google Workspace: in the Admin console, under Security, Authentication, 2-Step Verification, schedule enforcement with an enrolment period for new starters (from 1 day to 6 months), then exclude text message and phone call codes.
- Warn staff a week ahead with a one-page guide.
Week 3: remote access, banking and online tools
- Turn on MFA for the VPN and remote desktop, or remove unnecessary exposed access.
- Review authorised users, limits and dual approval of transfers with your bank.
- Enable MFA on every online tool, preferring single sign-on through your Microsoft or Google account where the tool supports it: one account to protect instead of ten.
Week 4: password manager, recovery and checks
- Roll out the password manager (see below).
- Write the recovery procedure and test it on one account.
- Check in the console that every account has two registered methods, and chase the stragglers.
- Offer passkeys to volunteers: they will gradually become the default.
The password manager underpins everything
MFA does not remove the need for good passwords: many services still have no second factor. The French data protection authority’s recommendation of 21 July 2022 sets, for a password used on its own, the equivalent of 12 characters mixing all four types, 14 without special characters, or a 7-word passphrase, chosen at random. It no longer recommends periodic changes for ordinary accounts, but keeps them for admin accounts.
Nobody can remember a hundred random passwords: ANSSI recommends giving users a password vault. Choose a business plan that lets teams share access without emailing passwords and lets you take back control when someone leaves, and protect the vault itself with a passphrase and a second factor. Our chapter on passwords, MFA and passkeys goes into the details.
Emergency accounts and recovery: the back door
Strong MFA will not stop an attacker who gets it reset. The Scattered Spider group, described by CISA, phoned IT help desks posing as employees to have passwords reset or MFA moved to a device they controlled. And in France, the CNIL fined France Travail, the public employment service, €5 million on 22 January 2026: attackers had taken over advisers’ accounts through social engineeringSocial engineeringManipulation techniques that get a person to bypass security themselves: revealing a password, approving a payment, opening a door or installing software., and the CNIL found their authentication arrangements were not robust enough.
Your recovery procedure should boil down to a few rules:
- Two registered methods per person, one of them not on their main phone.
- Two emergency admin accounts, reserved for emergencies, protected by a FIDO2 key and monitored, as Microsoft recommends.
- Backup codes printed or stored in the password manager, never in the mailbox.
- No reset on the strength of a phone call or email alone: call back on the number in the directory, approval by a manager, or in person.
- Automatic alert to the employee and the administrator whenever an MFA method changes.
- Access removed on an employee’s last day.
What ANSSI and the CNIL say
- ANSSI (2021 guide): prefer a possession factor, do not use SMS, provide a password vault, plan an access recovery method suited to the context.
- CNIL: the 2022 password recommendation, then a dedicated MFA recommendation adopted on 20 March 2025, which flags the use of employees’ personal phones and SMS codes as points to watch.
- Large databases: since 30 April 2025, the CNIL considers MFA required for remote access to databases covering several million people, and made it an inspection priority for 2026.
These recommendations are not laws, but they describe the state of the art the CNIL expects under the security obligation in Article 32 of the GDPR. After a breach, failing to enable MFA on sensitive access counts heavily against you. If your business falls within the scope of the NIS2 directive, see our NIS2 page too.
Your staff also need to know how to reject an unexpected approval and spot a fake login page: the “Passwords, MFA and passkeys” module of the KrakenShield Academy trains them in a few minutes, with realistic scenarios.
An approval request you were not expecting gets rejected, then reported. Always. Even at 11 pm, even if it comes back ten times.
Key takeaways
- A password on its own no longer protects anything: it leaks, gets reused, is stolen by an infostealer or typed into a fake site.
- Priorities: admin accounts, email, remote access and banking, before every other online tool.
- SMS beats nothing, but France’s ANSSI advises against it; only FIDO2 keys and passkeys stand up to a fake site.
- A password manager for the whole team is still essential: one long, unique password per service.
- Account recovery is the back door: emergency accounts, backup codes kept safe and identity checks before any reset.
Frequently asked questions
Is SMS two-factor authentication safe?
It stops the simplest attacks but remains fragile: texts can be intercepted, numbers hijacked through SIM swapping, and codes typed into a fake site. ANSSI, the French national cybersecurity agency, recommends not using SMS as an authentication factor. Keep it only where a service offers nothing better.
What is the difference between MFA and a passkey?
MFA adds a second factor to your password: a code, a notification or a key. A passkey replaces the password with a cryptographic key pair stored on your device and unlocked with your fingerprint, face or PIN. It combines two factors in one gesture and only works on the genuine site, which makes it phishing-resistant.
Is MFA mandatory for businesses?
There is no general legal requirement. But the GDPR requires security proportionate to the risk, the French regulator CNIL expects MFA for remote access to large databases, banks already apply strong authentication, and Microsoft enforces it on its admin portals. For an admin account, it is essential in practice.
What should we do if an employee loses their phone or security key?
They should tell IT straight away. The administrator removes the lost device from the account, checks the employee’s identity through an independent channel (a call-back to the known number, or in person), then helps them register a backup method or a new key. That is why everyone should always have two methods registered.
Should we still change passwords every 90 days?
Not for ordinary accounts: the CNIL no longer recommends periodic changes, which lead to predictable passwords. Change a password immediately if it is compromised, and regularly for admin accounts. A long, unique password kept in a password manager offers better protection.
Sources
- CNIL, Deliberation no. 2022-100 of 21 July 2022, recommendation on passwords (in French)
- CNIL, Recommendation on multi-factor authentication (deliberation no. 2025-019 of 20 March 2025, in French)
- CNIL, Guidance on strengthening the security of large databases (30 April 2025, in French)
- CNIL, Data breach: €5 million fine against France Travail (29 January 2026, in French)
- ANSSI, Recommendations on multi-factor authentication and passwords (ANSSI-PG-078, 8 October 2021, in French)
- Cybermalveillance.gouv.fr, 2025 activity report (March 2026, in French)
- CERT-FR, Threats linked to cookie theft and countermeasures (CERTFR-2022-CTI-005)
- CISA, Scattered Spider, advisory AA23-320A (updated 29 July 2025)
- Microsoft Learn, Mandatory MFA for Azure and Microsoft 365 admin portals
- Microsoft Learn, Security defaults in Microsoft Entra ID