Cybersecurity platform hosted in continental Europe

Audit your website. Train your team.

KrakenShield (Kraken Shield) is a European cybersecurity platform for professionals: four audits to understand what to fix on your website, and training to build everyday cybersecurity habits, on your own or with your team.

Free sign-up, no credit card, no commitment.

  • Non-destructive by default
  • Data in Europe
  • Authorization required
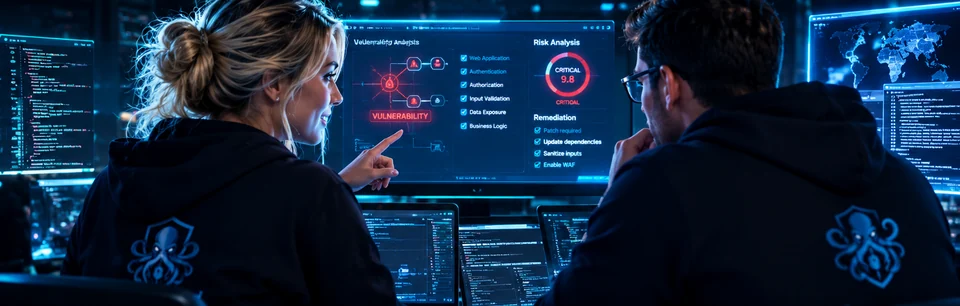
Belinda and Nestor analyzing a vulnerability
Discover KrakenShield

See the risk. Take back control.

Join Belinda and Nestor to discover four ways to understand your exposure and prioritise your next move.

45 seconds · English video
Kredit coins, the currency of KrakenShield audits
10 free Kredits

Promo code: BETATEST2026

Become a beta tester
Read the summary

KrakenShield examines your exposed systems and SSL/TLS configuration, observes cookies, trackers and consent journeys, analyses security mistakes, secrets and vulnerable dependencies in your code, and tests your defences within an authorised scope. Reports present findings and prioritised fixes. Join the beta with code BETATEST2026 to receive 10 free Kredits.

Open the video page →

  • A+ → FA clear gradeper domain, every finding with a recommendation
  • 0 linesof code uploadedthe agent scans on your server
  • 100%hosted in Europeat IONOS, no data ever resold
  • 4 auditson one platformTLS, privacy, code and penetration testing
One platform

Everything you need to hold your attack surface.

TLS configuration, source code and privacy: one platform to understand your exposure and prioritize fixes. Explore the available capabilities and those rolling out.

The KrakenShield octopus guards a shield bearing a padlock: SSL/TLS and surface audit.01
External surface and SSL/TLS, graded with the SSL Labs methodologyAvailable

Surface audit

Assess, without touching anything, the TLS configuration of your domains: versions, cipher suites, certificates, and HTTP security headers.

  • Clear grade from A+ to F
  • Certificate chain & expiry
  • HSTS, CSP, X-Frame-Options headers
Learn more
Nestor

Surface audit

Read the transcript

A surface audit checks what your website exposes online: certificates, encryption and web protections. I spot visible weaknesses and help you understand what needs fixing.

The KrakenShield octopus inspects a cookie with a magnifying glass: privacy audit.02
Cookies, consent and third-party trackersAvailable

Privacy audit

Discover what your homepage stores and contacts before any choice, after rejecting and after accepting cookies. Technical observations to guide your GDPR work, without claiming legal certification.

  • Cookies, browser storage & third-party trackers
  • Three consent journeys compared
  • Prioritized actions & exportable report
Learn more
Nestor

Privacy audit

Read the transcript

A privacy audit observes cookies and trackers before a choice, after rejection and after consent. I show you what changes and which privacy protections need checking.

The KrakenShield octopus catches a bug on a laptop showing code: code analysis.03
A lightweight agent on your server, your code stays homeAvailable

Code analysis

One command on your server is enough: the agent analyzes your code in place, detects secrets and generates a CycloneDX SBOM of your dependencies. These are checked against an extensive database of known vulnerabilities, powered by OSV and its reference sources. Only the inventory and findings are sent back: your source code stays with you.

  • One-line deploy (curl | bash)
  • CycloneDX SBOM: component & version inventory
  • Known vulnerabilities: CVEs, GHSAs & ecosystem advisories via OSV
  • Updated database, with OSV fallback when the local copy is stale
  • Static analysis, secrets & dependencies, without uploading source code
Learn more
Nestor

Code analysis

Read the transcript

Code analysis looks for security mistakes, exposed secrets and vulnerable dependencies. My diagnosis helps you prioritise fixes and reduce risk. Your source code stays on your server.

The KrakenShield octopus throws a dart into the bullseye: penetration test.04
Orchestrated, on authorization, non-destructiveAvailable

Penetration test

A console-driven pentest: reconnaissance, exposed ports, TLS, vulnerabilities, sensitive resources and backdoor detection. Go further with SQL injection detection, hidden content discovery and brute-force simulation to check your login protections.

  • Verified scope & authorization, limited rates
  • SQL injection, hidden content & brute force: explicit opt-in
  • Backdoors / webshells & anti-DDoS posture without load testing
  • Kill-switch: stop anytime
Learn more
Nestor

Penetration test

Read the transcript

A penetration test puts your defences to the test, with your authorisation. I look for exploitable weaknesses, including around login pages, then highlight the fixes to prioritise.

Coming soon
The KrakenShield octopus holds a padlock marked with an atom: post-quantum cryptography.05
Cloudflare hardening via API

Post-quantum encryption

Assess your TLS readiness for the quantum era and apply a modern encryption posture on your Cloudflare edge, via API.

  • Post-quantum readiness score
  • TLS 1.3, HSTS, modern policy
  • Tracked & reversible changes
Our method

A clear framework, from scope to remediation.

KrakenShield automates the whole path (scope, analysis, prioritization, follow-up) so you get consultant-grade results without waiting for a consultant.

Belinda and Nestor reviewing a vulnerability and risk analysis
  1. 01

    You set the scope

    SSL and privacy: any public website. Penetration testing: you prove the domain is yours and accept the mandate, nothing runs outside that scope.

  2. 02

    We analyze

    The analysis runs in the background, isolated, with zero risk to your production.

  3. 03

    We prioritize

    Not a tool dump: graded, explained results with the concrete fix to carry out.

  4. 04

    You fix and track

    Apply the fixes, re-run the audit whenever you want and watch your grade climb.

Why KrakenShield

The rigor of a firm, the speed of a platform.

A report gathering dust protects no one. We tell you what is exposed, why it matters and what to fix first, without your data ever leaving Europe.

Create your account

European sovereignty

100% European, from hosting to AI

Your domains, audit results and conversations with our assistants never leave the European Union. The whole chain runs on European providers.

  • IONOSHosting and dataEuropean Union
  • Mistral AIOnline assistantsParis
  • BrevoEmail deliveryParis
  • GDPR compliant
  • Encrypted at rest and in transit
  • Data never resold

Nothing runs without your go-ahead

Proof of domain control and an accepted authorization mandate before any penetration test. Every action is checked server-side, timestamped and logged.

Findings, not logs

Every issue is graded, explained in plain words and paired with a recommended fix, ranked by real risk. You know exactly where to start on Monday morning.

A pentester’s method, minus the waiting list

Proven, non-destructive methods, industrialized: re-run an audit after every fix instead of waiting for the next engagement.

Belinda

Belinda

PhD in cryptography, special forces veteran

Born and educated in Europe, Belinda wrote her thesis on post-quantum cryptography, then served eight years in the special forces with an electronic warfare unit. That is where she learned to break encrypted communications under pressure, and to stay calm when every light turns red.

Back in civilian life, she hunts down fragile certificates and outdated protocols, and trains AI models to spot what looks wrong in an encrypted stream.

« Weak encryption is an armoured door with the key under the mat. »

  • Post-quantum cryptography
  • TLS and certificates
  • AI anomaly detection
  • Crisis management
Nestor

Nestor

Former hacker, now on the defence side

At twenty, Nestor toured government websites without an invitation. The stunt earned him five years in prison, which he used to complete a master’s degree in computer security and read everything there was on neural networks.

These days he only attacks with written authorization. He thinks like an attacker because he used to be one, and he teaches AI to look for your flaws before anyone else finds them.

« I know the back door: I used to walk through it. »

  • Penetration testing
  • Application security
  • Offensive AI
  • Social engineering

Getting started with Kredits

Kredits are the units used for audits and training. Each action’s cost is shown before confirmation: it depends on the audit type and, for code analysis, the size scanned.

  1. Create your account and apply the welcome offer available in the form.
  2. Confirm your email, then choose an audit or your training. Your balance and expiry dates remain available in My Kredits.
  3. For an audit, Kredits are reserved during analysis and deducted when it succeeds. You keep them if it fails technically.

A TLS audit checks encryption and certificates. A privacy audit examines cookies and trackers. Code analysis needs an agent; penetration testing requires a verified scope and authorisation.

Start with the Kredits granted by the promotional code, subject to its conditions: no purchase is needed to use them. To go further, buy a pack in My Kredits, with secure Stripe payment and an invoice.

Let’s take action

Create your free account.

Access your console to choose an audit or explore Academy training. You stay in control of the Kredits you use.

  • Audits: explained findings and fixes to prioritise
  • Academy: train yourself or your team
  • Data hosted in Europe

Already have an account? Sign in

Free sign-up, no credit card, no commitment.

12 characters minimum

Belinda

Contact us

A question, a project, a partnership? Write to us: the team answers by email, usually within one business day.

Your details are only used to answer you. Do not include passwords or vulnerability details.